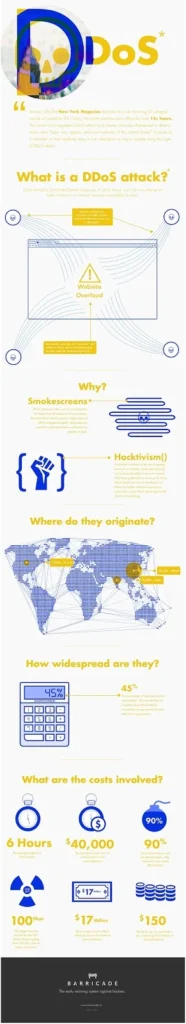
A distributed denial-of-service (DDoS) attack tries to make a website, network or online service unavailable to legitimate users by overwhelming or disrupting the resources it needs to respond. The traffic can come from many systems at once, which is why filtering a single source is often not enough. This overview explains the impact and defensive response without providing instructions for launching an attack.
What users may notice
A service under a denial-of-service attack may load slowly, return errors or stop responding. Similar symptoms can also result from a routine outage, a local internet problem, a faulty deployment or an overloaded server. Users usually cannot determine the cause from a browser error alone. Check the organization’s official status page or support channel before assuming an attack is occurring.
Why DDoS incidents are difficult
Organizations depend on capacity at several layers: network connectivity, servers, applications and upstream providers. A flood that consumes bandwidth differs from traffic that exhausts an application’s processing or storage resources. Attack traffic can be mixed with normal requests, and defenders have to preserve legitimate service while identifying and limiting the harmful load. Affected organizations may need assistance from their internet provider, hosting company, content delivery network or specialist mitigation service.
How service owners prepare
Useful preparation includes documenting critical systems, keeping provider contacts and incident procedures current, monitoring service health, and knowing which provider supports traffic filtering or scaling. A response plan should define who can make changes, who communicates with customers, and what evidence should be recorded. Organizations should follow their incident response plan and coordinate with network and hosting providers rather than making rushed configuration changes without testing.
What customers should do
If a service is unavailable, try its official status page, wait before repeatedly submitting a form or payment, and avoid links claiming to offer a special recovery download. Do not run tools advertised as a way to “fight back”; they can expose your device or worsen the disruption. If you operate the affected service, contact your hosting or DDoS-protection provider promptly and preserve relevant logs. CISA recommends activating incident-response plans and working with service providers to mitigate an attack and restore normal operations.
A DDoS event affects availability; it does not by itself prove that customer accounts or data were accessed. Treat any separate security notice seriously, but rely on verified communications from the service.
Reference: CISA: understanding and responding to DDoS attacks.
Related reading: Operation Hong Kong: Anonymous’ 2014 Cyberattack Campaign in Context.

